Multi Cloud Compliance in the Real World: Examples, Mistakes, and What It Actually Costs
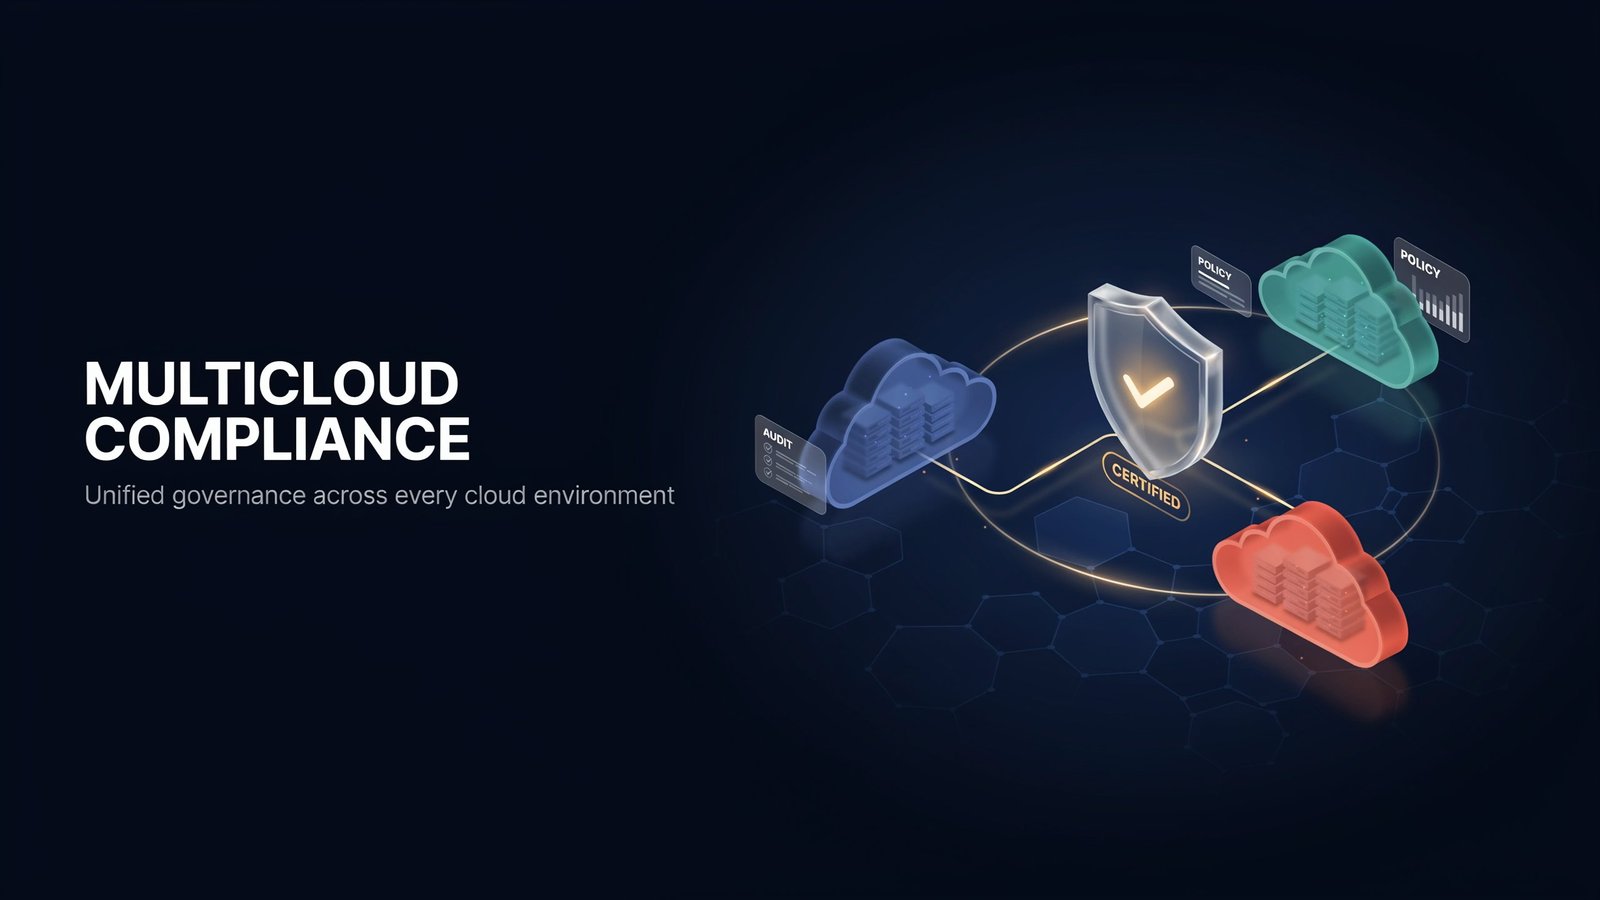
Multi cloud compliance means enforcing consistent security and regulatory controls across multiple cloud providers with unified policies and automated evidence. Done well, it cuts audit prep from weeks to days and prevents breach-level fines. Done poorly, it produces failed audits, six-figure penalties, and exhausted teams.
The question nobody asks until it is too late
Here is a conversation I have had more than once. A founder tells me, "We passed our SOC 2 last year, so we are compliant." Then I ask one question: "Does that include the Azure environment you added in March?" Silence.
That silence is where cross-cloud compliance risk lives. Companies expand across clouds for good business reasons: cost, client requirements, better services. But compliance scope rarely expands with it. The result is an environment that is certified on paper and exposed in practice.
In this post, I will walk through real cloud security examples, the mistakes I see teams repeat, what staying compliant across providers actually costs, and how to think about its return on investment. If you are a leader trying to justify the budget, this one is for you.
What cloud compliance means when money is on the line
What is cloud compliance, in business terms? It is proof. Proof to regulators that you follow the law. Proof to enterprise customers that their data is safe with you. Proof to insurers, auditors, and your own board that the risk is managed.
Compliance in cloud computing is never static, because your environment changes daily. Running multiple providers raises the stakes further: every additional platform multiplies the places a control can quietly fail while the paperwork says everything is fine.
The frameworks you already know, SOC 2, ISO 27001, HIPAA, PCI DSS , GDPR, all apply to your entire environment, not the convenient half of it.
Cloud security examples: three failure stories
Let me share three anonymized but real cloud security examples that show how cross-cloud compliance breaks.
Example one: the certified half. A SaaS company held a clean SOC 2 report covering AWS. They later added GCP for analytics, holding the same customer data. Their next audit flagged the entire GCP estate as out of scope for controls they claimed to enforce. The remediation took four months and delayed a funding round.
Example two: the encryption exception. A healthcare platform enforced encryption at rest in their primary cloud. A secondary cloud, used for backups, ran with provider defaults, which meant some storage was unencrypted. Under HIPAA, that is a reportable exposure. The fix took days. The paperwork took months.
Example three: the ghost administrator. A fintech's CI/CD service account had admin privileges in Azure, created during a migration and never revoked. An ISO 27001 auditor found it. Least-privilege violations like this are among the most common findings in multi cloud security reviews, and among the easiest to exploit.
In each case, the technical fix was trivial. The expensive part was the audit fallout, the customer explanations, and the delayed roadmap.
Notice the pattern. None of these teams lacked skill or tools. They lacked consistency across clouds, which is the entire game when you run more than one provider.
The five mistakes I see teams repeat
- Certifying one cloud and claiming the whole business. Auditors and customers increasingly ask for environment-wide scope. Partial certifications are losing their value.
- Trusting the shared responsibility model too far. AWS's shared responsibility model and its Azure and GCP equivalents make clear: providers secure the infrastructure, you secure everything you configure. "The cloud is compliant" is not a compliance strategy.
- Running evidence collection manually. Screenshots and spreadsheets cannot keep pace with cloud change, and they collapse under continuous-monitoring expectations in modern frameworks.
- Letting controls drift between providers. A policy enforced in one cloud and approximated in another is a finding waiting to happen. Define once, implement everywhere.
- Treating compliance as an annual event. This discipline is continuous. The NIST Cybersecurity Framework and the CSA Cloud Controls Matrix both assume ongoing monitoring, not yearly reviews.
What multi cloud compliance actually costs
Let us talk money, because this is where leaders make the wrong trade.
The cost of doing it manually: Internal audit preparation for a single framework typically consumes weeks of senior engineering time. Multiply that by two or three clouds and two or three frameworks, and you are spending a meaningful percentage of your team's year on screenshots and spreadsheets. Add external audit fees, and the number climbs fast.
The cost of getting it wrong: Failed audits delay enterprise deals. I have watched a seven-figure contract stall for a full quarter because a prospect's security team asked for evidence that did not exist yet. GDPR penalties can reach into the millions. HIPAA violations carry per-incident fines plus mandatory breach notification. And the reputational cost of telling a customer their data sat unencrypted in a forgotten cloud? No spreadsheet captures that.
The cost of doing it right: A unified cross-cloud compliance program, with automated evidence collection and continuous monitoring, typically pays for itself within one or two audit cycles. Teams I have worked with cut audit prep from six weeks to under a week, and cut findings dramatically because drift gets caught in days, not months.
How to calculate the ROI
When I build the business case with leadership, I use a simple frame:
- Hours of engineering time saved per audit cycle, times your loaded hourly cost
- Deals unblocked or accelerated by current, environment-wide certifications
- Avoided penalties and breach costs, weighted by your realistic probability
- Reduced tooling sprawl, because one unified program replaces several per-cloud processes
One more factor most teams forget: insurance and customer contracts. Cyber insurance questionnaires increasingly ask about continuous monitoring and environment-wide controls. Weak answers raise premiums or void coverage. Strong, documented cross-cloud controls do the opposite.
Strong multi cloud security and compliance is not a cost center. It is a sales asset. Enterprise buyers increasingly send security questionnaires before they send purchase orders, and a clean, current, environment-wide compliance posture shortens those sales cycles measurably.
Key Takeaways
- Failures in this space usually come from scope gaps: one certified cloud hiding an uncertified one.
- Real-world failures follow patterns: encryption exceptions, ghost admins, and drift between providers.
- Manual compliance costs more than automation once you count engineering hours across clouds and frameworks.
- Compliance failures delay deals and trigger penalties. Unified compliance accelerates sales.
- ROI comes from saved audit hours, faster enterprise deals, and avoided fines. It typically materializes within two audit cycles.
Frequently Asked Questions
What is multi cloud compliance, in one sentence?
It is the ongoing work of enforcing the same security and regulatory controls across all your cloud providers, with unified policies and automated evidence that proves it to auditors and customers.
Is multi cloud compliance more expensive than single cloud compliance?
It costs more upfront because scope grows, but a unified program costs far less than running separate per-cloud efforts. Automation narrows the gap quickly, usually within one or two audit cycles.
Which cloud security compliance standards matter most for enterprise sales?
SOC 2 and ISO 27001 open the most enterprise doors. Healthcare buyers require HIPAA, payment flows require PCI DSS, and European customers expect GDPR alignment. Scope across every cloud you operate.
What is the most expensive compliance mistake across clouds?
Scope gaps. Certifying one cloud while customer data flows through another has triggered failed audits, delayed funding, delayed deals, and regulatory exposure in real companies I have worked with.
How do I justify cross-cloud compliance spending to my board?
Frame it as revenue protection and acceleration: audit hours saved, enterprise deals unblocked, and fines avoided. Compliance posture now appears in procurement decisions, making it a sales asset, not overhead.
When should we bring in outside help?
When your team is spending weeks per audit, when you are adding a second or third cloud, or when a framework deadline is approaching and internal capacity is thin. External expertise is usually cheaper than a failed audit.
The bottom line
Multi cloud compliance is where security meets revenue. Get it right, and audits become routine, enterprise deals move faster, and regulators stay satisfied. Get it wrong, and you fund the lesson yourself, in fines, failed audits, and stalled sales cycles.
If you want to know where your environment actually stands, tkxel offers a free multi cloud security consultation. Their team reviews your architecture, identity setup, and compliance posture across AWS, Azure, and GCP, then hands you a prioritized risk map, usually within one to two weeks. It is the clearest first step I know between "we think we are compliant" and "we can prove it."
0 Comments