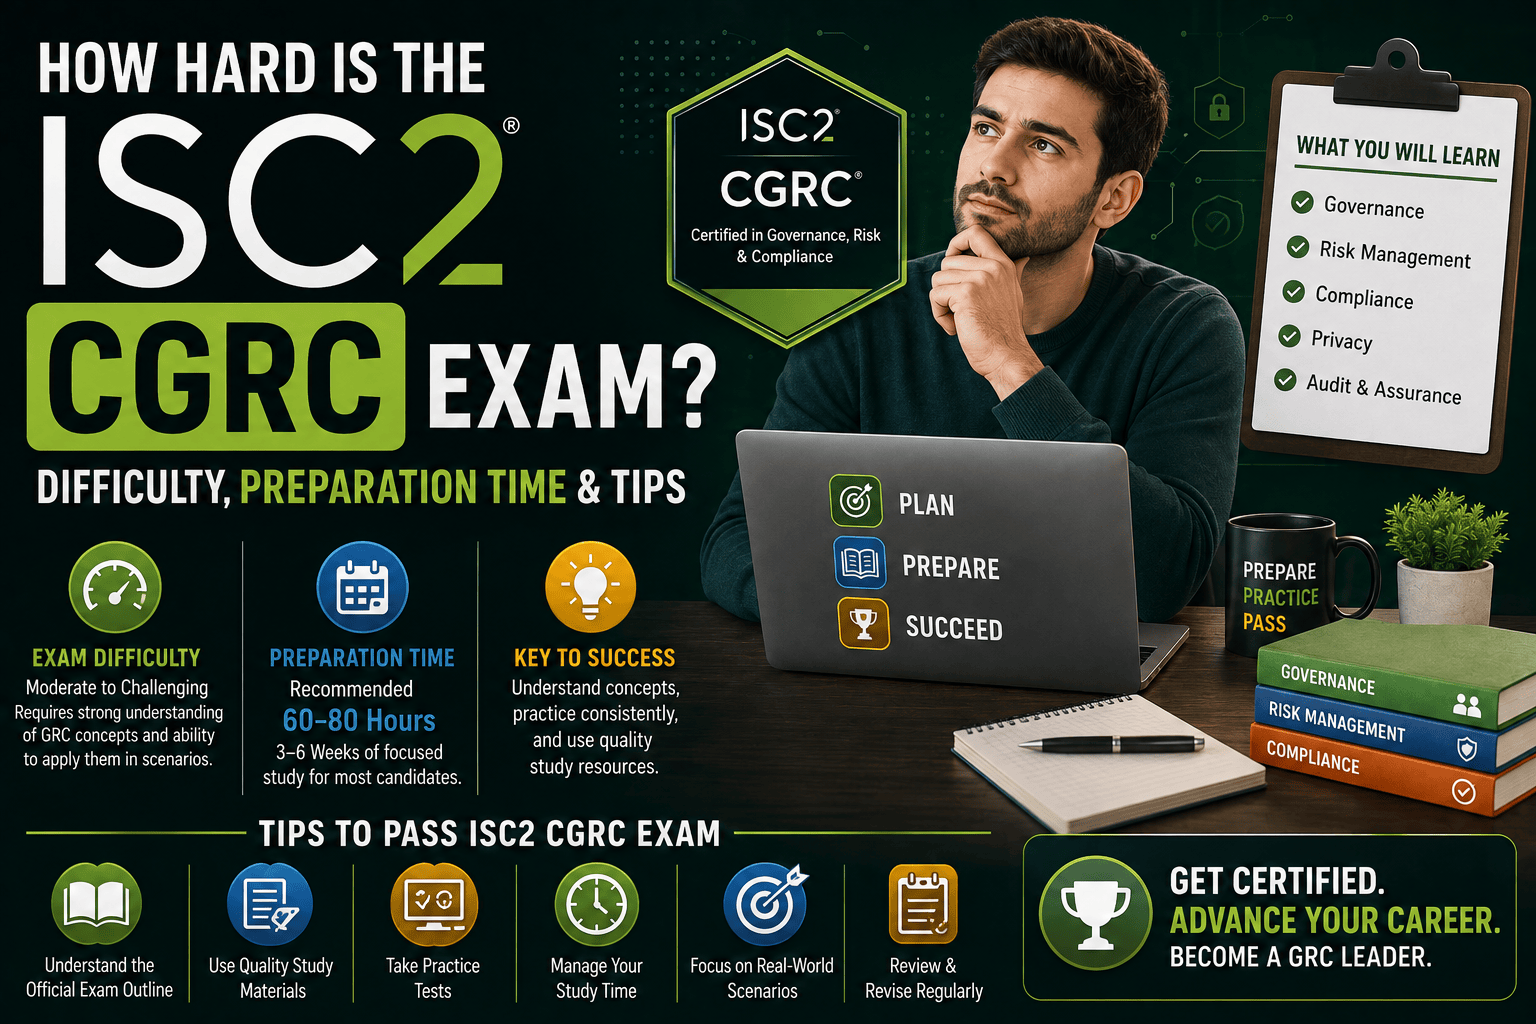
How Hard Is the ISC2 CGRC Exam? Difficulty, Preparation Time & Tips
The ISC2 CGRC exam is generally considered moderately difficult to difficult, especially for candidates who have limited experience with governance, risk management, compliance, auditing, security controls, and information-system authorization.
CGRC stands for Certified in Governance, Risk and Compliance. The certification is aimed at professionals who apply security and privacy frameworks, evaluate controls, support compliance decisions, assess risk, and maintain information systems within regulatory requirements. ISC2 requires two years of relevant experience for the full credential, although candidates without that experience can pass the exam first and become an Associate of ISC2.
The exam is challenging because it tests judgment across the complete GRC lifecycle rather than simple terminology memorization.
ISC2 CGRC Exam at a Glance
Exam Detail | Current Information |
Certification | Certified in Governance, Risk and Compliance |
Vendor | ISC2 |
Level | Experienced professional |
Exam Length | 3 hours |
Number of Items | 125 |
Question Types | Multiple choice and advanced item types |
Passing Score | 700 out of 1000 |
Language | English |
Experience Requirement | 2 years |
Exam Delivery | Pearson VUE testing center |
ISC2's current CGRC outline remains the version effective from June 15, 2024. The exam contains 125 items and allows three hours.
How Difficult Is the CGRC Exam?
For someone already working in governance, risk, compliance, information assurance, authorization, or auditing, the exam is manageable with structured preparation.
For someone coming entirely from a technical cybersecurity background, it may feel considerably harder.
CGRC questions require you to understand areas such as:
- Governance
- Security and privacy frameworks
- Risk management
- System boundaries
- Control selection
- Control implementation
- Assessment and audit
- Compliance decisions
- Continuous compliance
- Change management
The challenge is often deciding which action is most appropriate at a particular stage of the GRC lifecycle.
Several answers may appear reasonable, but only one best matches the process and context.
What Does the CGRC Exam Cover?
The current exam contains seven domains:
Domain | Weight |
Security and Privacy Governance, Risk Management, and Compliance Program | 16% |
Scope of the System | 10% |
Selection and Approval of Framework, Security, and Privacy Controls | 14% |
Implementation of Security and Privacy Controls | 17% |
Assessment/Audit of Security and Privacy Controls | 16% |
System Compliance | 14% |
Compliance Maintenance | 13% |
Implementation of Security and Privacy Controls currently has the highest weighting at 17%, although the exam is relatively balanced across all seven domains.
That balance means candidates cannot safely ignore any major section.
What Makes CGRC Difficult?
Framework Knowledge
Candidates need familiarity with multiple frameworks and standards rather than one single methodology.
The current outline references examples including:
- NIST
- ISO/IEC
- COBIT
- FedRAMP
- PCI DSS
- FISMA
- GDPR
- HIPAA
- CMMC
You do not necessarily need to memorize every control from every framework, but you should understand why frameworks exist and how they affect risk, controls, compliance, and authorization.
Process Sequencing
CGRC heavily tests lifecycle thinking.
You should understand the logical flow from:
Governance → Scope → Control Selection → Implementation → Assessment → Compliance Decision → Maintenance
If you confuse the stage at which a particular activity belongs, scenario questions become difficult.
Risk-Based Decision Making
You must understand concepts such as:
- Residual risk
- Risk acceptance
- Risk mitigation
- Risk transfer
- Compensating controls
- Risk registers
- POA&M
- Control effectiveness
The exam often rewards the answer that best reflects governance and organizational risk rather than the most technically aggressive security action.
How Long Should You Study for CGRC?
Preparation time varies substantially by experience.
Experienced GRC Professional: 4–6 Weeks
Someone already working with controls, audits, frameworks, risk assessments, or compliance documentation may need approximately 40–60 focused study hours.
Most preparation will involve aligning existing knowledge with ISC2 terminology and the seven-domain structure.
Cybersecurity Professional New to GRC: 6–10 Weeks
Someone with security experience but limited formal governance or compliance exposure may need 60–100 hours.
More time should be spent learning:
- Framework structure
- Assessment processes
- Risk documentation
- Compliance decisions
- Authorization terminology
Beginner With Limited Security Experience: 10–12+ Weeks
A complete newcomer should expect a longer learning curve.
CGRC is not designed as an entry-level certification. ISC2 requires two years of professional experience for full certification, although candidates can use the Associate of ISC2 route if they pass before meeting that requirement.
A Six-Week CGRC Study Plan
Week 1: Governance and Risk
Focus on:
- GRC principles
- Risk frameworks
- Regulatory requirements
- Privacy
- Organizational roles
- Security objectives
Understand how business requirements influence security and compliance decisions.
Week 2: System Scope and Control Selection
Study:
- System boundaries
- Information types
- Risk-impact levels
- Baseline controls
- Inherited controls
- Control tailoring
- Control enhancements
Pay close attention to why controls are selected rather than memorizing names.
Week 3: Control Implementation
Focus on the highest-weighted domain.
Study:
- Control implementation
- Compensating controls
- Documentation
- Policies and procedures
- Risk registers
- POA&M
- Residual risk
Week 4: Assessment and Audit
Practice understanding:
- Assessment planning
- Evidence
- Interviews
- Examination
- Testing
- Findings
- Risk-response actions
- Final assessment reports
Week 5: Compliance and Maintenance
Review:
- Compliance decisions
- Risk posture
- Formal documentation
- Stakeholder communication
- Change management
- Continuous monitoring
Week 6: Practice and Review
Complete:
- Mixed practice questions
- Timed sessions
- Weak-domain revision
- Framework comparisons
- Scenario-based review
How to Use Practice Questions Effectively
Practice questions are especially useful for CGRC because they teach you to distinguish between several plausible answers.
Cert Empire provides ISC2 CGRC exam questions that can support exam-focused review alongside the official ISC2 outline, framework documentation, and hands-on GRC experience.
After every question, ask:
- Which CGRC domain does this belong to?
- What stage of the lifecycle is being tested?
- Why is the chosen action appropriate now?
- Why are the alternatives less suitable?
- Is the question asking about risk, compliance, implementation, or assessment?
This reasoning is more valuable than memorizing answers.
Know the Exam Format
ISC2 states that CGRC includes both multiple-choice and advanced item types.
Across ISC2 exams, advanced items may include:
- Charts or tables
- Calculations
- Ordering
- Drag-and-drop
- Hotspot questions
- Scenario-based formats
Candidates need a scaled score of at least 700 out of 1000 to pass.
Do not interpret 700 as exactly 70%. ISC2 uses scaled scoring.
Common CGRC Preparation Mistakes
Avoid:
- Memorizing framework names without understanding their purpose
- Focusing only on NIST
- Ignoring privacy concepts
- Treating CGRC like a purely technical security exam
- Skipping control-assessment processes
- Confusing risk acceptance with risk mitigation
- Ignoring system-scope decisions
- Memorizing practice-question answers
- Neglecting the official exam outline
The exam requires process understanding rather than isolated facts.
Tips for Passing CGRC on the First Attempt
Focus on the why and when behind every activity.
Understand who is responsible for decisions, what documentation is required, and where an action belongs in the lifecycle.
Also practice distinguishing terms such as:
- Assessment vs authorization
- Risk identification vs risk treatment
- Baseline vs tailored controls
- Residual risk vs inherent risk
- Compliance decision vs continuous monitoring
Finally, use the official blueprint as your study checklist. ISC2 explicitly recommends exam outlines to help candidates identify what they need to master before testing.
Conclusion
The ISC2 CGRC exam is challenging, but it is very manageable for candidates with relevant GRC or information-security experience and a structured preparation plan.
Its difficulty comes mainly from the breadth of the seven domains, framework knowledge, risk-based decision making, control lifecycle concepts, and scenario questions where several answers can appear correct.
Experienced GRC professionals may prepare in four to six weeks, while security professionals new to formal governance and compliance may need six to ten weeks or more.
The strongest preparation strategy is to study the official ISC2 outline, understand the entire GRC lifecycle, practice framework-based scenarios, review mistakes carefully, and connect exam concepts with real-world risk and compliance activities.
FAQs
Is the ISC2 CGRC exam difficult?
Yes, it can be moderately difficult to difficult because it tests seven broad GRC domains and expects candidates to apply frameworks, risk-management principles, controls, assessment, and compliance concepts.
How many questions are on the CGRC exam?
The current CGRC exam contains 125 items and allows three hours for completion.
What score do you need to pass CGRC?
ISC2 requires a scaled score of 700 out of 1000.
How much experience is required for CGRC?
ISC2 requires two years of cumulative relevant experience in one or more CGRC domains. Candidates without it can become an Associate of ISC2 after passing and then gain the required experience.
How long should I prepare for CGRC?
Experienced GRC professionals may need four to six weeks, while candidates newer to governance and compliance may require six to ten weeks or longer.
Read More: How to Use an Exam Simulator to Pass Your Certification Exam
0 Comments